Cybersecurity and ransomware recovery. When seconds count.
Ransomware, breaches, data theft. Our incident response team contains them in hours. Across every engagement we've ever run, nobody has paid a ransom.
Live Incident Response
Contain. Recover.
No ransom. Ever.
Every incident runs the same playbook: isolate, capture forensics, spin up a clean environment, restore from immutable backups. We've never told a client to pay a ransom. Not once.
Our Services
Full-spectrum cyber defense.
Incident Response
Containment and triage right away, then the full response. Available 24/7/365.
Digital Forensics
We preserve the evidence, reconstruct the attack and deliver legal-grade reporting.
Ransomware Recovery
We restore from immutable backups with no ransom paid, and keep a complete forensic chain of custody.
Security Audits
Penetration testing, vulnerability assessment, and red-team simulations.
Compliance
HIPAA, SOC 2, PCI DSS, ISO 27001. We handle the paperwork and the gaps.
Threat Intelligence
Real-time IOC feeds and behavioral analytics, plus proactive threat hunting.
Response Guarantees
Hard SLAs. No wiggle room.
Threat Intelligence
We see threats before they reach you.
Our SOC analysts watch 24 live threat intelligence feeds and check IOCs against your environment in real time. A new LockBit variant drops, and your defenses update in minutes.
- 24 active threat intelligence feeds
- Automated IOC blocking and sinkholing
- Behavioral anomaly detection via SIEM
- Zero-day response within hours of disclosure
Prevention
Stop the incident before it starts.
Most incidents we respond to start with a phishing email or an unpatched website. Relay scans mail links against Google Safe Browsing, and Pulse scans WordPress sites for malware, vulnerabilities and rogue administrators.
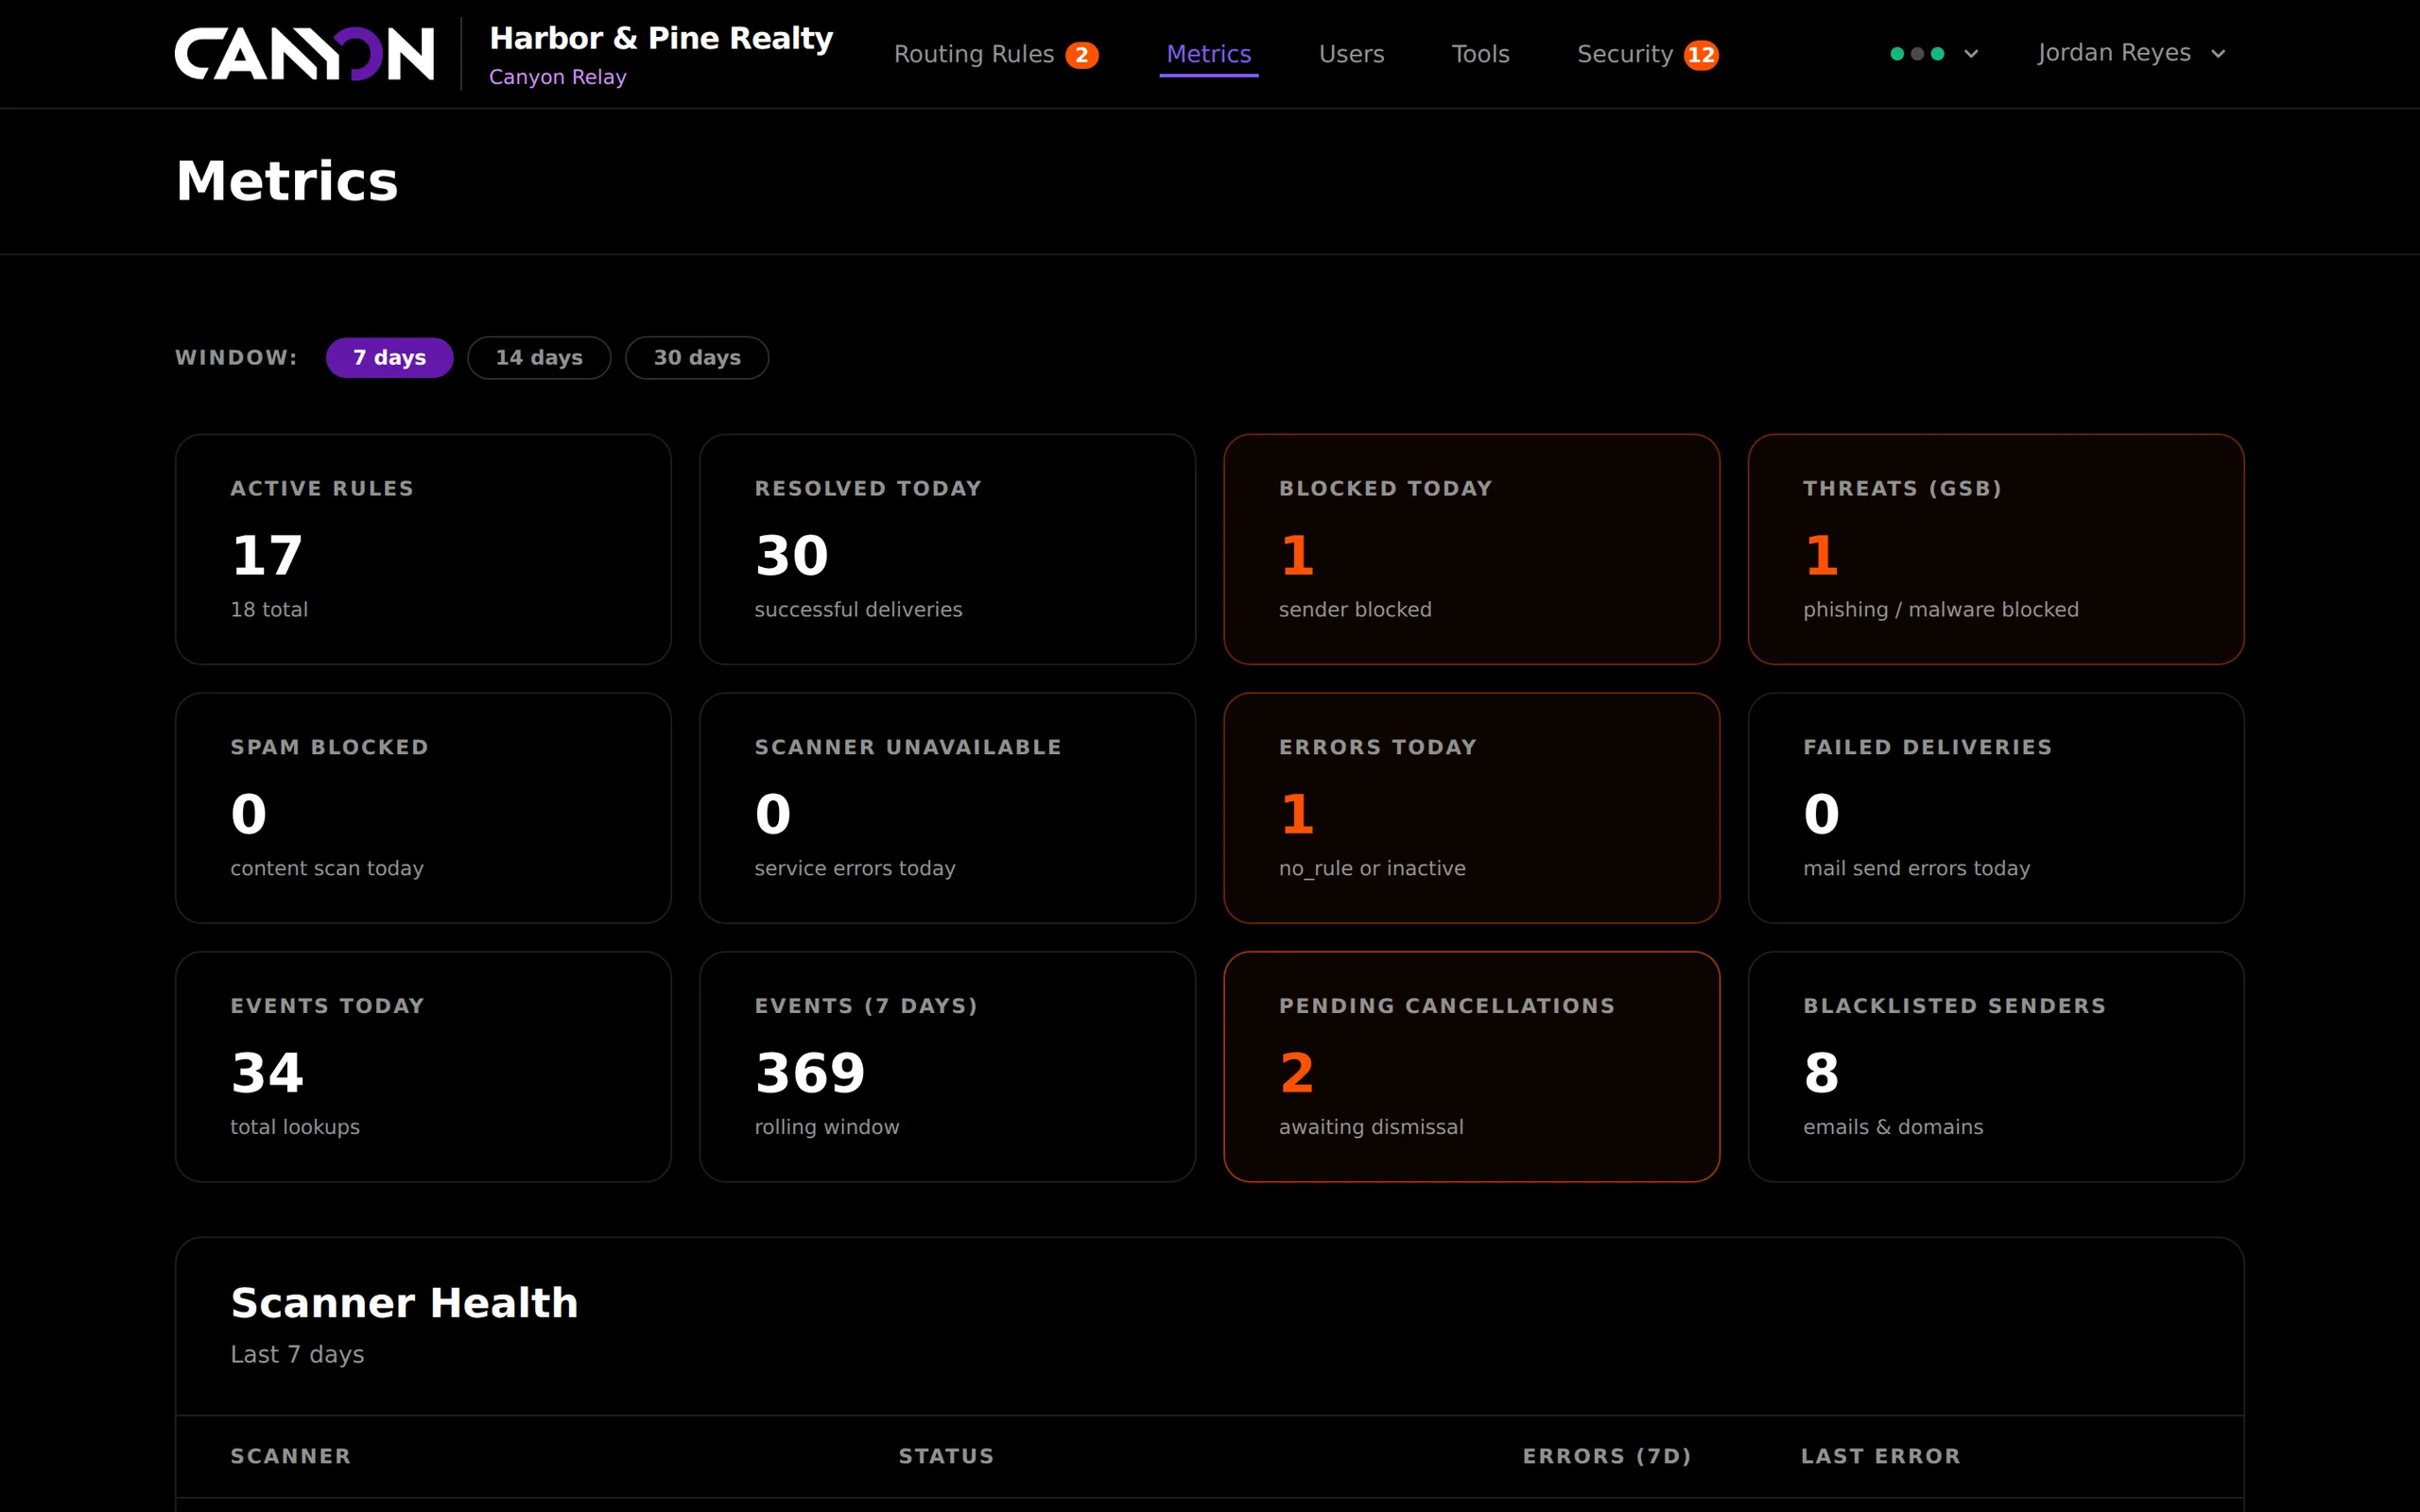 Secure email routing platform
Canyon Relay
Branded email forwarding that scans every message for phishing and spam before it reaches your team. Explore Relay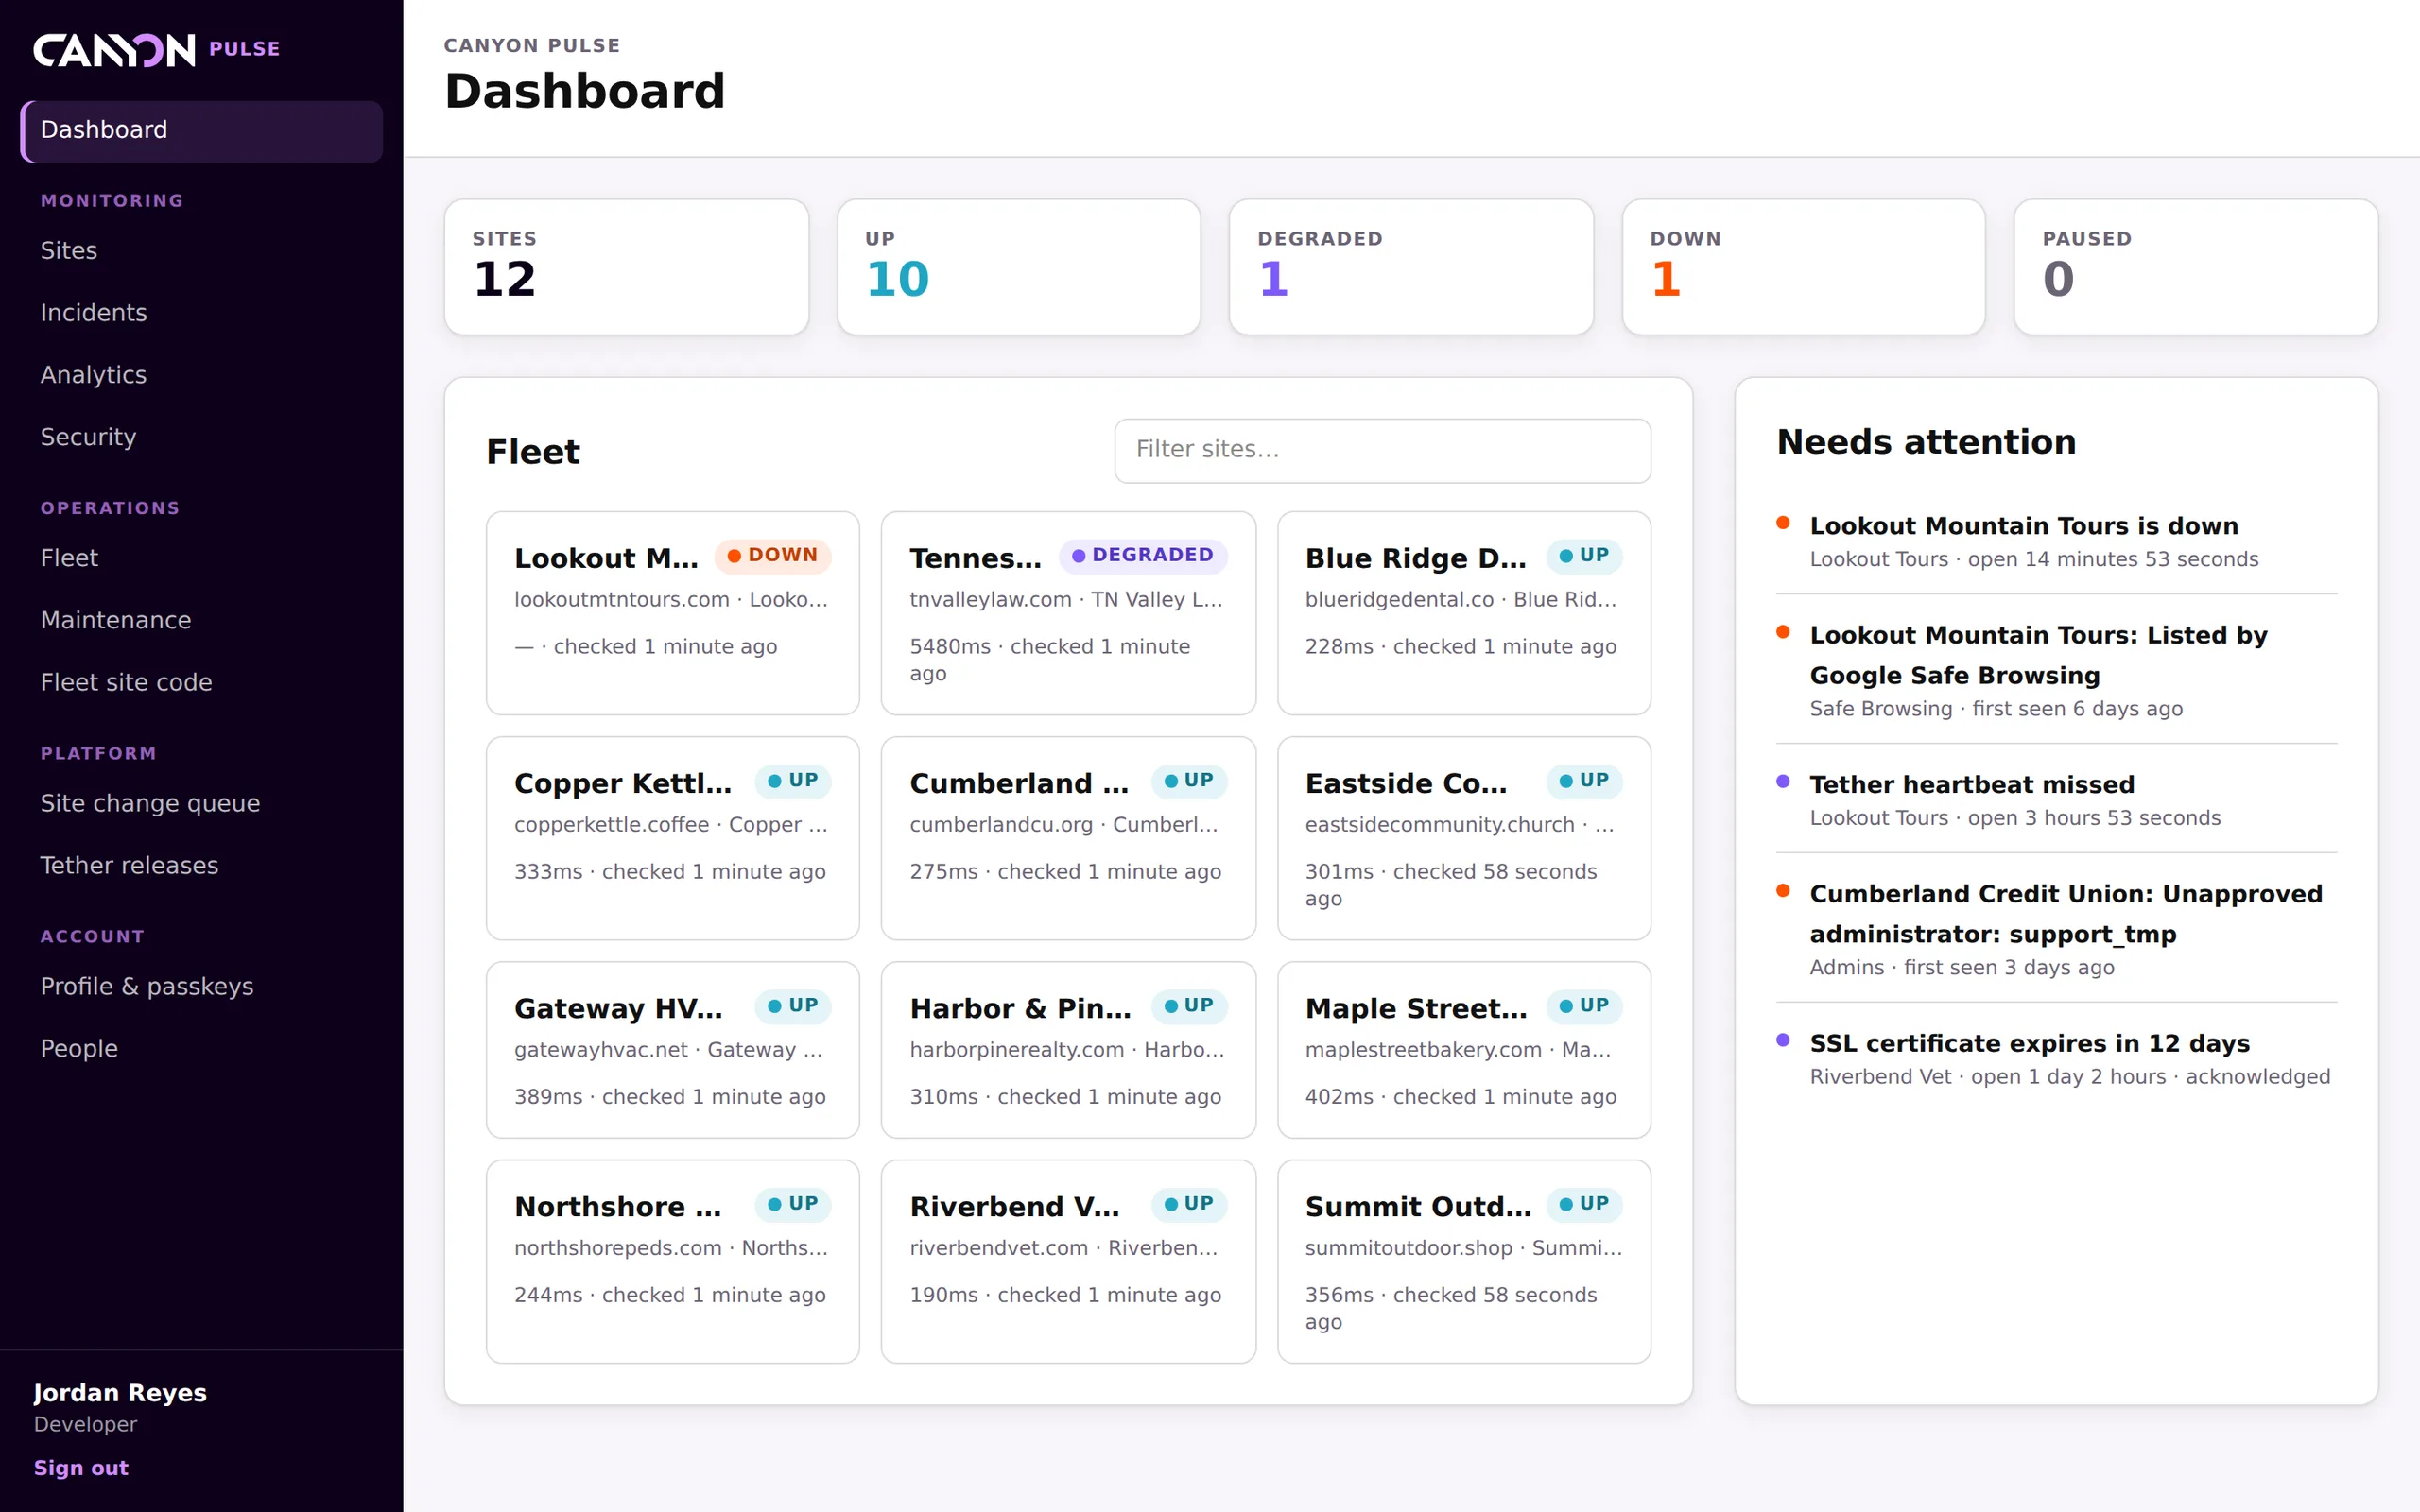 WordPress operations platform
Canyon Pulse
Uptime, SEO, security and maintenance for every WordPress site we manage, in one panel. Explore Pulse
Security Emergency?
Don't negotiate. Call us first.
Active ransomware gets more expensive by the minute. Our response team is standing by 24/7/365, and containment starts within 15 minutes of your call.